Solidity Audit · internal tool
Bounty Hunter
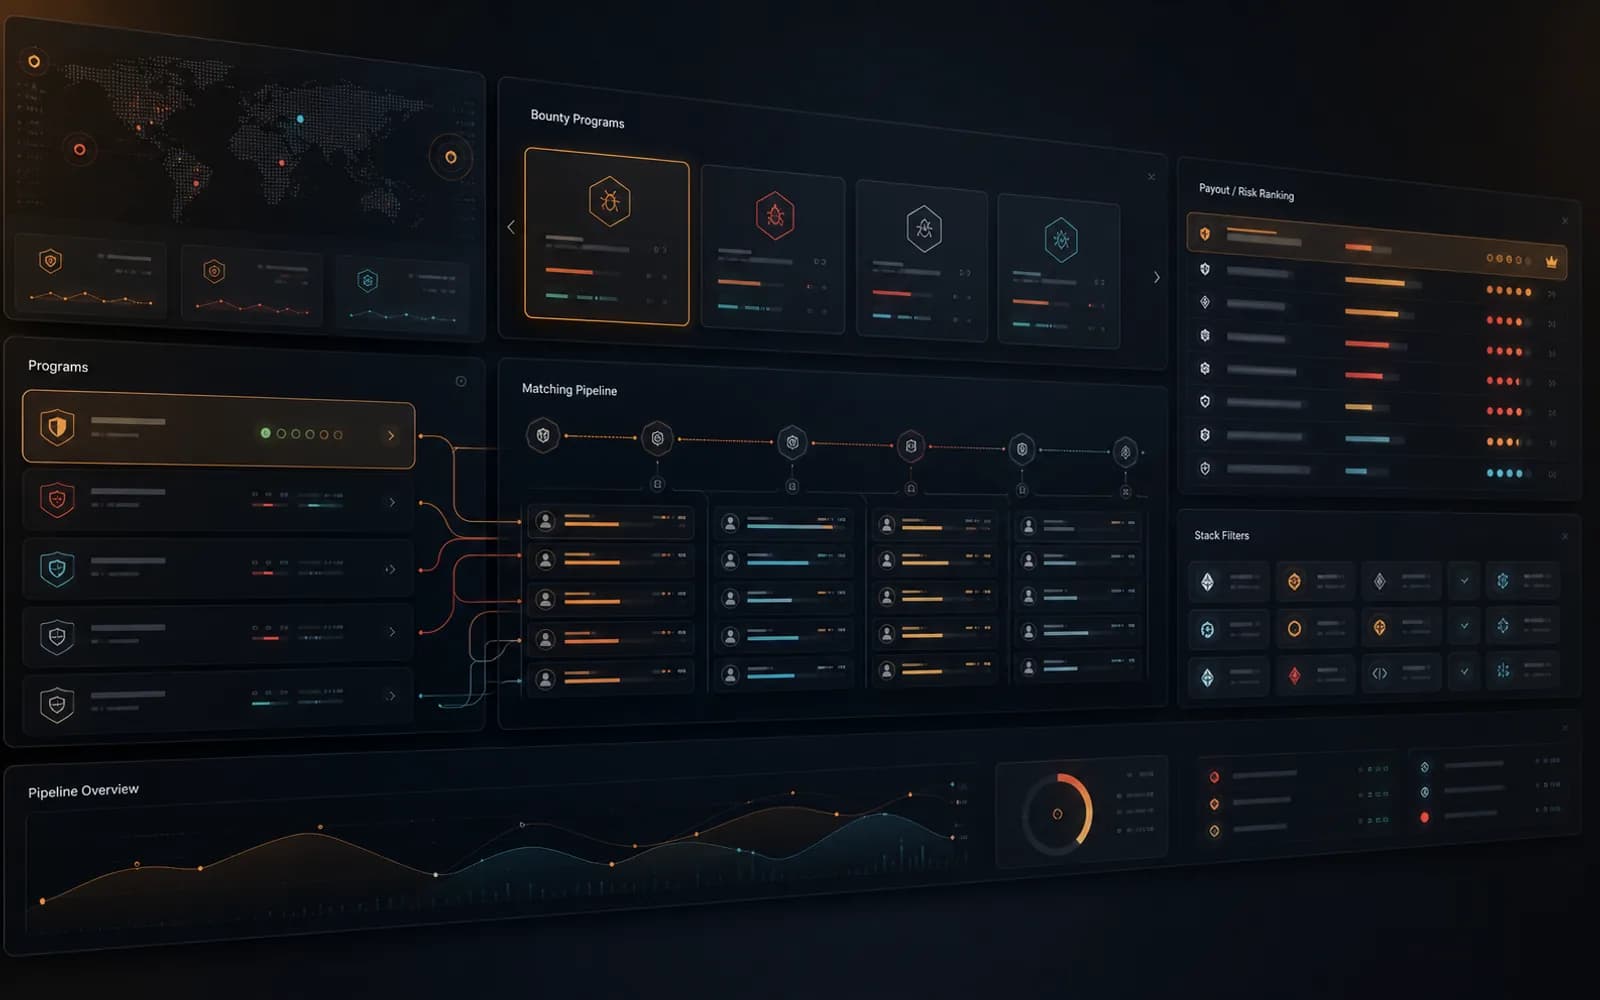
Internal aggregator: pulls Immunefi/Code4rena/Sherlock bounties weekly, ranks by stack/payout/severity for our auditor network.
Editorial presentation
The public deployment renders a loading error; keep only the editorial cover until a sanitized internal capture exists.
Project context
Internal tool we use to track active bug bounty programs (Immunefi, Code4rena, Sherlock, HackenProof) and match them with the auditor profiles in our network. Filters by stack, payout range and severity. Powers the agency's audit pipeline.
Business Impact
The strongest proof points from the project.
Before
Active bounty programs change weekly. Manually matching auditor profiles against eligible programs is slow and the agency misses good opportunities.
What I built
Aggregator that ingests Immunefi, Code4rena and Sherlock feeds, normalizes payout and stack, and produces ranked match lists per auditor.
Result
Internal prototype
Stack
Need to validate a similar bottleneck?
Describe the workflow that is manual, slow or hard to measure today. You get focused questions and a verifiable first milestone — without locking you into an endless project.